01
OpenAI API, Anthropic Claude, Google Gemini, & Azure OpenAI powering multi LLM orchestration.
FEATURED PROJECT | AGENTIC SYSTEMS & AI SAFETY
Solving high operational risk, PII data leakage, and unmonitored LLM hallucination threats in enterprise generative AI deployments.
100%
Enterprise Policy Enforcement
Real-Time
Hallucination & Threat Monitoring
Multi-LLM
Model & Provider Support
Cryptographic
Audit Logging & Lineage
Industry Pain Points & Core Challenges
Enterprise AI teams, developers, and compliance officers traditionally struggle to deploy LLMs safely exposing organizations to hallucination risks, prompt injection vulnerabilities, and compliance failures. These operational bottlenecks leave enterprises vulnerable to data leaks, unmonitored agent behavior, regulatory fines, and slowed product adoption.
Strategic Solution & Platform Architecture
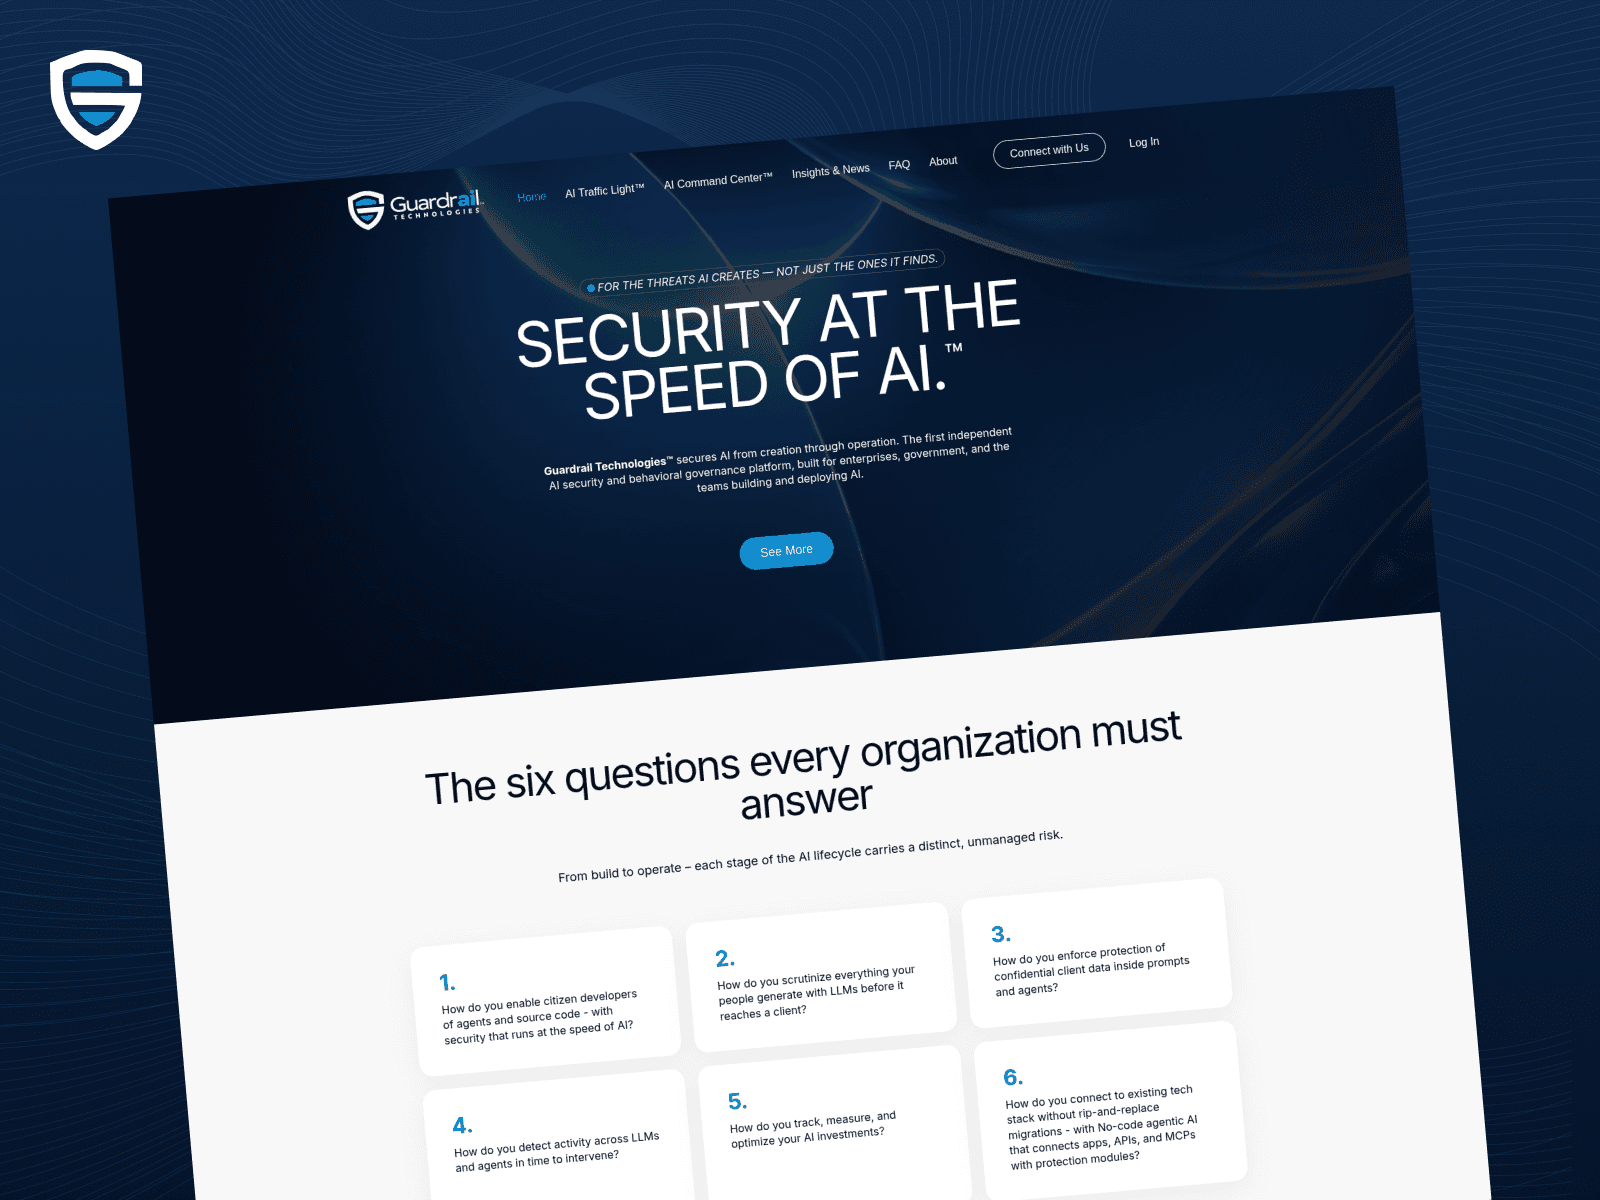
GuardRails AI provides an enterprise trust layer where AI model interactions are automatically monitored, sensitive data is redacted, and rule governance is applied across live system workflows. GuardRails connects engineering teams, security officers, and compliance auditors in a unified, audit ready ecosystem.
User Journey & Operations
01
User prompts and system inputs enter the platform, where prompt injection defense screens for malicious payloads.
02
The data protection engine scans inputs, redacting PII and sensitive enterprise data prior to LLM processing.
03
Queries pass to the AI layer (OpenAI, Anthropic, Gemini, Azure) while the policy engine validates output accuracy and rules.
04
Auto generate audit trails and logs featuring real time threat alerts, policy citations, and system compliance history.
Architecture & Technology Stack
01
OpenAI API, Anthropic Claude, Google Gemini, & Azure OpenAI powering multi LLM orchestration.
02
React.js Frontend delivering responsive management dashboards for live policy monitoring.
03
Node.js API Backend handling scalable application business logic and routing.
04
Python Engine providing continuous evaluation, real-time hallucination checking, and prompt defense algorithms.
05
Cryptographic Audit Infrastructure ensuring verifiable logging for compliance officers.
06
AI Trust Layer™ delivering central policy enforcement across all agentic workflows.
Technology Stack
Outcomes & Business Impact
Real time policy enforcement and prompt defense drastically reduce manual auditing requirements, allowing teams to scale AI safely.
Catching prompt injections, sensitive data leaks, and hallucinations early prevents security breaches and regulatory non-compliance.
Every model interaction retains cryptographic logs, policy validation records, and threat audit histories for enterprise verification.
Next step
Let's discuss how we can help bring your idea to life.